
Содержание
- Vendor list что это
- THE SIMPLE-KEY TYPE
- FILES
- SEE ALSO
- BUGS
- AUTHOR
- Index
- What is a Vendor List?
- Vendor list что это
- Approved vendor list | procurement
- THE SIMPLE-KEY TYPE
- FILES
- SEE ALSO
- BUGS
- AUTHOR
- Index
- Vendor Identifier — что это за программа на Андроид?
- Vendor Identifier — что это такое?
- Что делать?
- Заключение
This type of verification is used when the vendor has a single secured key that must be used to sign the Release file. The following items should be present Fingerprint The PGP fingerprint for the key. The fingerprint should be expressed in the standard notion with or without spaces. The —fingerprint option for gpg (1) will show the fingerprint for the selected keys(s). Name A string containing a description of the owner of the key or vendor. You may put the vendor name and it’s email. The string must be quoted with «.
Vendor list что это
The package vendor list contains a list of all vendors from whom you wish to authenticate downloaded packages. For each vendor listed, it must contain the corresponding PGP key fingerprint, so that APT can perform signature verification of the release file and subsequent checking of the checksums of each downloaded package. To have authentication enabled, you must add the vendor identification string (see below) enclosed in square braces to the sources.list line for all sites that mirror the repository provided by that vendor.
The format of this file is similar to the one used by apt.conf. It consists of an arbitrary number of blocks of vendors, where each block starts with a string telling the key_type and the vendor_id .
Some vendors may have multiple blocks that define different security policies for their distributions. Debian for instance uses a different signing methodology for stable and unstable releases.
key_type is the type of the check required. Currently, there is only one type available which is simple-key.
vendor_id is the vendor identification string. It is an arbitrary string you must supply to uniquely identifify a vendor that’s listed in this file. Example:
THE SIMPLE-KEY TYPE
This type of verification is used when the vendor has a single secured key that must be used to sign the Release file. The following items should be present Fingerprint The PGP fingerprint for the key. The fingerprint should be expressed in the standard notion with or without spaces. The —fingerprint option for gpg (1) will show the fingerprint for the selected keys(s). Name A string containing a description of the owner of the key or vendor. You may put the vendor name and it’s email. The string must be quoted with «.
FILES
SEE ALSO
BUGS
See the APT bug page . If you wish to report a bug in APT, please see /usr/share/doc/debian/bug-reporting.txt or the reportbug (1) command.
AUTHOR
APT was written by the APT team .
Index
What is a Vendor List?
| Закладки на веб-сайте Проследить за страничкой | Created 1996-2023 by Maxim Chirkov Добавить, Поддержать, Веб-мастеру |
Vendor list что это
The package vendor list contains a list of all vendors from whom you wish to authenticate downloaded packages. For each vendor listed, it must contain the corresponding PGP key fingerprint, so that APT can perform signature verification of the release file and subsequent checking of the checksums of each downloaded package. To have authentication enabled, you must add the vendor identification string (see below) enclosed in square braces to the sources.list line for all sites that mirror the repository provided by that vendor.
Approved vendor list | procurement
The format of this file is similar to the one used by apt.conf. It consists of an arbitrary number of blocks of vendors, where each block starts with a string telling the key_type and the vendor_id .
Some vendors may have multiple blocks that define different security policies for their distributions. Debian for instance uses a different signing methodology for stable and unstable releases.
key_type is the type of the check required. Currently, there is only one type available which is simple-key.
vendor_id is the vendor identification string. It is an arbitrary string you must supply to uniquely identifify a vendor that’s listed in this file. Example:
THE SIMPLE-KEY TYPE
This type of verification is used when the vendor has a single secured key that must be used to sign the Release file. The following items should be present Fingerprint The PGP fingerprint for the key. The fingerprint should be expressed in the standard notion with or without spaces. The —fingerprint option for gpg (1) will show the fingerprint for the selected keys(s). Name A string containing a description of the owner of the key or vendor. You may put the vendor name and it’s email. The string must be quoted with «.
FILES
SEE ALSO
BUGS
See the APT bug page . If you wish to report a bug in APT, please see /usr/share/doc/debian/bug-reporting.txt or the reportbug (1) command.
AUTHOR
APT was written by the APT team .
Index
| Закладки на веб-сайте Проследить за страничкой | Created 1996-2023 by Maxim Chirkov Добавить, Поддержать, Веб-мастеру |
Vendor Identifier — что это за программа на Андроид?
Приветствую друзья, сейчас у нас тема — приложение Vendor Identifier на Android. Моя задачка — выяснить что же это все-таки за прога.. зачем нужна.. может это вообщем вирус? Такс ребята, не будем гадать, а начинаем разбираться!
Vendor Identifier — что это такое?
Начал копаться в вебе. Инфы ребята не так и много.. но кое что все же узнал:
Vendor Identifier — непонятное приложение, предположительно указывает рекламу. Не считая этого может быть очередное — Incartech, вероятнее всего также маркетинговое.
Один юзер удалил Vendor Identifier, пишет что заморочек нет, реклама пропала. Но он также удалил и Incartech. Что самое увлекательное.. чел пробовал все — чистить систему антивирусами, всякими чистилками, но эффекта ноль. Также пробовал.. перепрошивать телефон. Но в конечном итоге реклама все равно была. Да, такое тихо может быть — маркетинговое приложение идет интегрированным в прошивку, в особенности нередко явление встречается на китайских телефонах.
Вообщем.. Vendor Identifier либо Vendor ID — это значит идентификатор вендора. Ну а вендор это ..что-то вроде компании, производителя. Есть еще такое как Product Identifier — это практически тоже самое, только идентификатор уже не производителя, а конкретно модели.
Другими словами можно прийти к выводу, что заглавие спецом изготовлено так, чтоб вводить нас в заблуждение. Чтоб пошевелили мозгами что норм приложение и угрозы не представляет.. ну и не задумывались удалять..
Ребята, инфы нет вообщем больше. Я прочесал веб — ничего не нашел.
Что делать?
Я вижу два варианта:
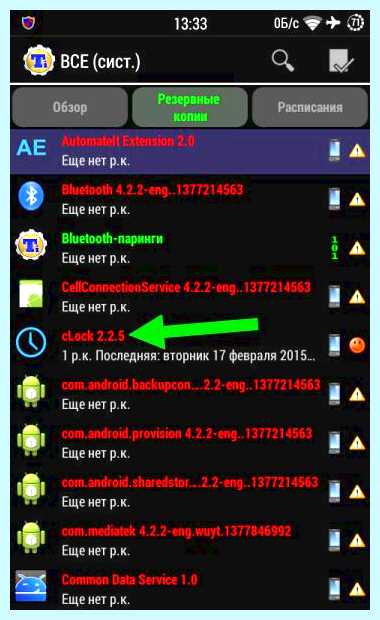
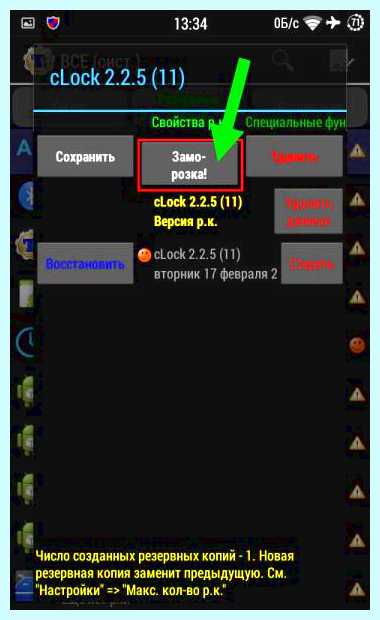
- Заморозить приложение с помощью Titanium Backup. Но нужны рут права. После заморозки стоит протестировать телефон пару дней, если все будет норм, то можно и удалить приложение.
- Проверка телефона антивирусами. Возможно что сейчас, когда вы уже читаете, то антивирусы находят это нежелательное ПО. Все же ведь это не вирус, это просто стоковое приложение, которое показывает рекламу.
В титаниуме просто выбираете приложение, например cLock 2.2.5, нажимаете по нему:
И потом уже будет кнопка заморозки приложения:
Если будете проверять антивирусом, то советую использовать известный, например Касперский, Доктор Веб, Нод.
Также оч советую обратится на форум 4PDA. Если вы там найдете свою модель телефона — то напишите в теме, просто опишите свою проблему. Если вашей модели нет — напишите в теме похожей. Могут помочь, не вы одни с этой проблемой.
Хотя вот пишут что лучший антивирус это Antiy AVL, он обнаруживает до 99.7% угроз в реальном времени. Насколько правда — не знаю, но название антивируса не особо известное.. по крайней мере мне..
Так, стоп, вот узнал что есть такое приложение как AirPush Detector, которое сканирует все приложения на наличие рекламы. Стоит попробовать.
Заключение
К сожалению толком ничего узнать не получилось, так как инфы тупо нет. Но вывод можно сделать такой:
- Vendor Identifier — вероятнее всего рекламное приложение. Название специально такое, чтобы вводить в заблуждение, типа это важная системная прога.
- С удалением могут быть проблемы. Если рут права есть — оч хорошо, тогда морозьте титаниумом или сразу удаляйте. Если рута нет — сканируйте телефон популярными антивирусами, например Касперский, Доктор Веб, Нод. Может какой-то уже способен определить это приложение и удалить его.
- Стоп. Важно. Приложение может само восстанавливаться. Поэтому при наличии рут прав — не удаляйте его, а именно морозьте титаниумом. Тогда оно теоритически не сможет восстановиться.
- Дополнительно можете просканировать телефон такими прогами как AirPush Detector, Malwarebytes.
В общем ребята, на этом все. Сори, что мало написал, но в интернете реально инфы оч мало. Удачи вам и добра!
Похожие статьи
-
Содержание Qualified Vendor List что это за драйвер? Что это такое? Для чего это нужно? Вывод Qualified Vendor List — что это за драйвер? Описание…